Learning about firewalls and network security is no easy chore. While a wealth of knowledge exists across the web, few domains can translate complex network security concepts into easily-digested lessons for beginners. Likewise, troubleshooting firewall issues often leads to old, obsolete forum responses and dead ends. You’re in luck.
The Firewalls.com YouTube library is continuously growing and packed to the brim with how-to’s, tutorials, troubleshooting guides, and more. Like a treasure trove full of SonicWall and Sophos solutions, Firewalls.com customers and visitors alike are sure to find the answers to their questions.
Who makes the videos?
We do! Right here in the office. Our video series is produced, edited, and narrating by our rockstar team of engineers and architects. If you’re the type of person that wants the answer straight from the horse’s mouth, then this is the channel for you. Our video makers are certified SonicWall and Sophos engineers with over a decade of combined experience in real world network security management. Learn about firewalls from the guys that spend every day up to their eyeballs in network security! Our two narrators, Alan and Matt, are ready to show you the ropes.
A look at our editing desk.
Who decides what video topics to cover?
You do! We generate topics for our videos based on the top search terms in YouTube, Google, and the Firewalls.com website. We know the Internet has important questions and we want to answer them. If there’s a certain topic you want us to cover, let us know in YouTube comment sections or on social media.
Why the Firewalls.com channel?
We want you to learn about cyber security, so we’re not going to waste your time. We’re no pack of newbs that spend the first two minutes of every video introducing ourselves, begging for likes, and talking about our BFF’s new music project. Get in, get answers, and get back to being productive.
What’s in it for me?
Information, readily available and easy to follow. Our videos are made by screen capturing our network techs using the same reporting and monitoring programs that our customers use, in real time. There’s no magic wand waving behind slick edits or cuts.
Running dual monitors? Set one screen to our YouTube and the other screen to your work space and you can fix network security snafus side-by-side, at your pace.
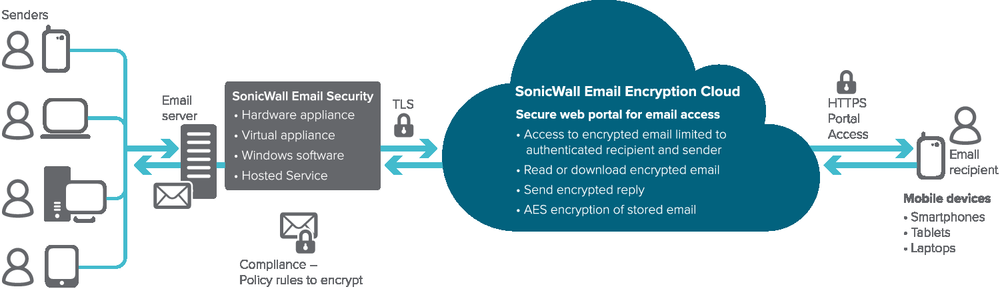
As Bring Your Own Device (BYOD) and Remote Access policies ramp up, so too does the mad dash to secure these new endpoints. Gartner predicted that by 2017, half of employers will require employees to supply their own device for work purposes. With so many fresh attack surfaces, employers scramble to assemble additional security layers that prevent data leakage and intrusions. The nature of BYOD proves challenging as devices in the wild show volatility without proper VPN and next-gen firewalls to lock down security.
Our solutions
Secure Mobile Access – Powerful, cost-effective secure mobile and remote access means that your users have access to applications wherever they’re working, so they stay productive and your company stays competitive.
SonicWall VPN – Ensure secure access to crucial applications for Android & iOS mobile devices using SSL and policy-based enforcement.
Next-Generation Firewalls – Next-Gen Firewalls provide you the power to execute cutting-edge security without your performance withering away.
Secure Remote Access – SonicWall Secure Remote Access solutions provide users with easy-to-use, secure, and clientless remote access to necessary resources on the corporate network.
Aventail SRA Connect Mobile – SonicWALL Aventail with Connect Mobile provides robust remote access solutions for smart phone users, with “in-office” access optimized for the device.
Trouble setting things up?
Firewalls.com provides a video library chock full of helpful how-to’s and troubleshooting guides. One of our certified engineers will provide the answers you crave to set up your remote access VPNs.
Firewalls.com is a value-added reseller of firewall appliances & a vendor of managed security and Firewall-as-a-Service support. Whether you’re looking to add an appliance to your security set-up or expand BYOD and remote access security, we provide solutions that get you secure and keep you secure. Contact our sales staff to answer questions you may have about your network, next-gen firewalls, or BYOD!
While it may sound like the final technique learned from Jackie Chan in a young adult movie, Hidden Cobra is actually the moniker given to state-sponsored actors executing cyber crime activities on behalf of the North Korean government. Before federal agencies reported on the activities of DPRK’s Hidden Cobra, the group was dubbed by the private sector as Lazarus Group or Guardians of Peace. Hidden Cobra is an extension of the North Korean government and targets both public and private entities with malware, data wipers, DDoS, and SMB worm tools. Known variants of Destover, Duuzer , and Hangman exploits are common modus operandi for Hidden Cobra. In addition, Hidden Cobra is notorious for their use of powerful DDoS attacks with their denial-of-service tool, DeltaCharlie.
Flushing Out the Snake
Hidden Cobra tends to target systems that run older, unpatched operating systems. The lack of firmware updates and plethora of attack surfaces found in obsolete Microsoft operating systems makes for low-hanging fruit the serpents are able to reach. A Technical Alert issued by the Department of Homeland Security and Federal Bureau of Investigation includes a database of recognized IP addresses and network signatures that they consider Indicators of Compromise (IOCs).
In addition to these IOC’s, DHS has published a Malware Analysis Report detailing the unique functionalities and common tactics demonstrated by Hidden Cobra actors.
Like real snakes, we have accumulated antidotes for a majority of the Hidden Cobra’s venoms. The following Common Vulnerabilities and Exposures (CVEs) are typical susceptibilities targeted by Hidden Cobra:
If Adobe Flash and Microsoft Silverlight are no longer necessary applications in your system, we highly recommend removing these programs completely.
Delta Charlie
Perhaps the most perilous tool operated by Hidden Cobra is their DDOS tool, DeltaCharlie. Sporting a standard botnet infrastructure, DeltaCharlie is used to launch DNS attacks, NTP attacks, and CGN attacks. DeltaCharlie disguises itself as a svchost service. The tool can download and operate macros, alter its own structure, and perform denial-of-service attacks on command.
If You’ve Been Targeted
Report the attack to DHS or FBI – Federal agencies are very interested in keeping tabs on the activity of North Korea’s state-sponsored cyber warfare adjuncts. You can report malware to the DHS here. They will certainly appreciate the information. Review visitor logs for IOCs – If you suspect Hidden Cobra is responsible for a raid on your network, cross-check records from your perimeter defenses against those IP addresses outlined in the Indicators of Compromise spreadsheet provided above. Run YARA– For readers unfamiliar with YARA, it is a tool developed by malware researchers to detect attack signatures. The Technical Alert issued by DHS and FBI include a variety of YARA rule definitions that can quickly and effectively track down signs of Hidden Cobra malware.
Preventing Hidden Cobra Attacks
Limit admin privileges – We’ve talked about this one before. When an attacker gets into your system, you don’t want everyone inside carrying around skeleton keys. Update your firmware – Hm. This one sounds familiar too. The straight-forward warning: the older your operating system, applications, or security patches, the more likely you are to be on the receiving end of cyber crime. This is as self-explanatory as comparing a modern digital security system to a string of rattling cans strung across the lawn. Go invite-only for your applications– The practice of whitelisting applications drastically cuts down potential attack surfaces in your network. In short, whitelisting is allowing only prescreened applications access to your system. If it’s not on the list, it stays outside. Leverage your firewall – Firewalls provide gateway security, content filtering, IP whitelisting, application controls, user groups, and more. There are a vast number of security options available to organizations to protect their data against the likes of Hidden Cobra, but most of them require a firewall appliance to operate. Think of your firewall as the command center of your security infrastructure. Next-generation firewalls are platforms designed to provide all of the security resources you need in one powerful appliance, known as Unified Threat Management.
Learn about UTMs offered by our manufacturer partners!
Stroll into any mid-range hotel with a flash drive in your pocket. Don’t bother with the old desktop computer in the lobby “business center.” Stop at the front desk, smile wide, and slap your USB device on the counter. Politely ask the guest services agent to print a document for you. If they direct you to the business center, claim that you tried it the previous night and couldn’t get it to work. Then observe.
Congratulations, you just slipped past the perimeter defense of a multi-billion dollar corporation. Let me lay out what happens next. The front desk staff takes your flash drive to the back, pops it into a USB port, and joyfully opens whatever file you ask them to.
I know this trick works because I’ve witnessed the scenario play out a thousand times. In a few instances, I was the unwitting hand guiding the thumb drive into a terminal. While most Firewalls.com blog posts shy away from anecdotes and keep individual histories at a professional arm’s length, this post is based on personal experience.
I worked in the hospitality industry for half a decade before shifting into the info sec market. This is what I learned.
Corporate Will Do the Leg Work for You
Okay, getting a file onto a machine was easy, but you’ve only infected a single computer on a closed network. Now what? Wait for corporate to do the heavy lifting.
Each night when the hotel audits their daily transactions, troves of data are gleaned from employee desktops and rolled up to the corporate servers for safe keeping. Your freeloading file needs only loiter on the network until about 2:00 or 3:00 in the morning, when corporate provides a free lift to the database where comprehensive financial data, transaction history, and confidential customer information for a multinational brand is stored.
Security Culture in 10 Minutes or Less
Hotel new hires typically sit through a series of training modules where the mainstays of employee on-boarding make their appearances: OSHA policy review, incident reporting, benefits programs, core values. If the brand is more forward-thinking, then somewhere in this hodgepodge of instructional videos is nestled the briefest touchpoint on cyber security.
Included in one training excursion I trudged through, the company splurged on commissioning Kevin Mitnick to narrate a nine-minute video on cyber crime. After a Spark Notes’ tier definition of social engineering, Kevin encourages new employees to address further email fraud questions to their direct supervisors.
Hoteliers Wear Many Hats, But None of Those are White Hats
Asking superiors for further information sounds reasonable, in a script. But I was a direct supervisor to over a dozen employees and was granted no special insight into preventing cyber crime. I was consistently preoccupied with expanding a repertoire of customer service, accounting, management, sales, payroll, quality control, HR, safety, facilities management, commercial kitchen, and plumbing skills. Hotel employees tend to be jacks of all trades at the expense of being even a journeyman in any specific talent. Specialists graduated away from the front lines quickly or were chased out when one of their duller skills failed to impress.
Perhaps further up the chain of command an answer could be uncovered? But my direct supervisor played audience to the very same training modules I watched. And his supervisors, now nearing the vice presidential or regional territory types, likely hadn’t seen a training video since before cyber crime was a credible threat. But surely further up the ladder, someone was watching over us. I’m certain that scouring LinkedIn or the company Outlook Address Book would inevitably turn up a VP of Technology or comparable title, but they were off in a lofty C-suite well outside the reach or even the zeitgeist of any ground-level employees looking for answers. For all intents and purposes, further information is impractical beyond utility if it exists at all.
Throwing the Baby Out With the Hogwash
An anecdote burned forever into my psyche involves an umbrella term that some corporate security wonk for one hotel brand took a liking to: hogwash. The term ‘hogwash’ and cyber security were married after an impassioned email in which the word was typed in bold font, in all capital letters, a total of 7 times. Several months later this diatribe lead to the introduction of a “hogwash button” on corporate email applications. At no point was it expounded exactly what ‘hogwash’ entailed or why reporting it proved crucial to company goals. The only instruction given was to delete and report any email that looked suspicious. The grounds for basing our suspicions, I suppose, were left to individual interpretation.
The Lesson to Be Learned
This is no simple attempt at picking on the hospitality industry. Instead, take this post as a wake-up slap. When discussing information security, there is a magnetic draw to discussing the healthcare industry, banking and financial institutions, or vulnerabilities haunting our governmental or infrastructure systems. But if we trot out the conversation to less flashy or FUD-inducing industries, we find a landscape brimming with entities just begging to be caught with their pants down. And while malware crashing the power grid makes for better thriller movie material, the hospitality industry still handles the confidential information of millions of travelers each day.
We must address the disconnect between security administrators in high towers and front-line employees operating in distant venues. Real human connections are necessary to impart the axioms of cyber security to ground level employees. This is personnel that doesn’t spend hours browsing Dark Reading or CNET.
Firewalls.com dedicates a lot of time and screen space to the cause of nurturing cyber security cultures in the office. We understand that even the most expensive and sophisticated security setup will fail if employees leave gateways wide open.
It’s time to revamp your library of training videos. It’s time to review SOPs with VPs who have occupied their positions since before the hazards of cyber crime fleshed out. It’s time to put cyber security on the same pedestals as accurate payroll, helpful customer service, and efficient logistics. And for the hotel industry in particular, it is time to leave the printing of boarding passes to airline kiosks.
Firewalls.com is a value-added reseller of firewall appliances & a vendor of managed security and Firewall-as-a-Service support. Our engineers are rigorously trained and certified by all of the major manufacturers that we partner with. Whether you’re looking to add an appliance to your security set-up or seek ongoing support from seasoned experts, we can provide the security solutions necessary to get you secure and keep you secure. Contact one of our knowledgeable sales staff to answer any questions you may have about your network, firewalls, or endpoint protection.
Metaphors for cyber security tend to gravitate towards the adversarial. We break into teams. We assign colors. We talk in terms of warfare. We man battle stations and try to push back against bad guys on active fronts. When discussing cyber security in the mindset of battle, of raiders and defenders, we find our line of thinking entrapped by binary outcomes of victory or defeat. However, framing the conversation in a fresh conceit fosters perspectives that may otherwise elude us.
While stock photo options for warfare are objectively more metal, we would like to investigate cyber security through the lens of epidemiology. Public health is a struggle that does not produce 100% winners or 100% losers. Instead, the goal revolves around mitigating infectiousness to the point that a disease no longer possesses the means to reproduce its efforts en masse, thus undercutting its capability to evolve into more sophisticated strains. This change in victory conditions births discussion of herd immunity.
What is herd immunity?
Herd immunity is a term used in epidemiology describing a secondary line of defense against infection that benefits individuals who cannot or have not gained immunity already. Vaccines are widely regarded as the primary security point against the spread of infectious diseases but thanks to the effects of herd immunity, those persons who cannot receive vaccination find shelter in a majority of the population being unable to spread disease.
Like malware, the first goal of a disease is to spread to the greatest number of hosts possible. A higher percentage of individuals infected by a disease grants that disease better potential to spread to new hosts. However, as the percentage of the population with immunity to that disease grows, the ability for the disease to spread softens.
Simply put, a disease with fewer bridges available to cross is limited in the distance that it can travel. Without delving too deep into epidemiology theory, a concept exists of thresholds that, once crossed, generally spell the end of outbreaks. In some cases, a combination of vaccination and herd immunity has led to the effective eradication of a disease. When was the last case of polio in the United States? The elimination of wild polio strains in certain regions is thanks to the fact that widespread immunity makes it more difficult for a polio outbreak to gain footholds in a human ‘herd’ and even more difficult for an outlier case to spin out of control.
In the past, human populations were concentrated in small, isolated groups. This meant that the extent of outbreaks were limited by geological factors. Spatial limitations no longer come into play in the modern era where humans can travel over mountains, across oceans, and hop between continents in a day’s time. Increased globalization and greater access to remote geographical regions mirrors the growth of interconnected, Internet-connected devices represented by the Internet of Things.
If we think of the Internet of Things as a population, we see a growing potential for infections to spread over new channels and pathways. The threat of more interconnected and heterogeneous mixing pushes higher the necessary threshold to trigger the benefits of herd immunity.
What does this have to do with me?
Framed in the perspective of public health, cyber security is an issue that concerns everyone.
If, like polio, over 90% of the Internet-connect populace were immune to ransomware, what motivation remains for hackers to continue developing exploits and writing malicious code? The cost-to-benefit analysis would be a quick calculation: the risk of deploying a cyber attack would outweigh the peanuts that attackers stand to make off the 5% of computers still exhibiting vulnerabilities.
Ensuring that 100% of devices are exploit-proof is a pipe dream. But if we apply the ideas of herd immunity, we can see that the goal never was absolute immunization. Instead, it would suffice to balance the equation in such a way that cyber crime is an untenable career.
The question then becomes how to make a life of cyber crime unappetizing.
Washing our hands of accountability
There is more to public health epidemiology than distributing vaccines until we pass thresholds.
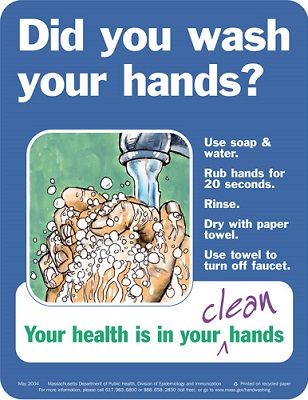
Consider the signs hanging in bathrooms all around the nation urging people to wash their hands. Spend one winter on a college campus and you’re sure to see plenty of warnings posted about hand washing, sneezing etiquette, and more. Over television and radio we receive public service announcements outlining precautions against the common cold and announcing schedules for flu shot season. Unfortunately, cyber security has no such mass public effort.
Often, the only groups preaching cyber health gospel are organizations that sell cyber security products or the creators of targeted software. This raises a question: where would we be if public awareness campaigns for cyber security were as prevalent as those for physical well-being?
Imagine strolling down a corridor and spotting a sign on the wall asking “Have you updated your firmware yet?”
Imagine a world in which school children were taught about phishing alongside the practice of covering their mouth when they cough.
Imagine if the end of every fiscal quarter heralded radio airtime dedicated to the whens, whys, and hows of data backup.
We may one day consider it myopic that mankind did not charge into the age of information on the wings of federally-funded education and information campaigns. The facts bear out that there is no such public health campaign for our cyber well-being. The onus for protecting our networks rests in our own hands. Despite a mirage of isolation, we find ourselves in a constantly more connected community.
A herd.
Firewalls.com continues to push for a larger umbrella of security for the Internet community not only because it benefits our own security, but that of the entire herd. Everyone has a stake in the outcome of this struggle. Encourage a culture of cyber security in your workplace. Host open discussions about Internet safety measures. Ensure that policies are in place and understood by employees.
While we do not all possess the skills and knowledge to be soldiers in a cyber crime war, we can take steps to provide the herd with a robust profile of immunization.
Whether you’re an organization of three employees or three thousand, you have joined a pool of potential victims. Firewalls.com has the expertise to make that pool a little shallower. Whether it be endpoint security suites, physical appliances, or managed services, cyber security solution providers want to guide you to the vaccines and best practices that simultaneously protect your organization and deny the bad guys another attack vector.
Firewalls.com is a value-added reseller of firewall appliances & a vendor of managed security and Firewall-as-a-Service support. Our engineers are rigorously trained and certified by all of the major manufacturers that we partner with. Whether you’re looking to add an appliance to your security set-up or seek ongoing support from seasoned experts, we can provide the security solutions necessary to get you secure and keep you secure. Contact one of our knowledgeable sales staff to answer any questions you may have about your network, our firewalls, or endpoint protection!