Secrets of the Mysterious & Ubiquitous Internet of Things

Without peeking, tell me the number of Internet-connected devices in the room with you. How about in the whole building? In 2017, it’s likely that the building itself is connected to the Internet. Whether it be through mobile-controlled thermostats, security cameras, or the traffic lights right outside your window, you live in a reality in which an Internet-capable device is likely within a few steps of you at any given time. This is the Internet of Things. And while the name doesn’t seem all that inspired (the term was coined by Kevin Ashton of MIT’s Auto-ID Center in 1999), it describes a nebulous world of Wi-Fi, RFID, and microcode that affects just about every transaction and interaction throughout your day.

As years pass, the Internet of Things grows. When an app is launched allowing you to refill your dog’s food bowl while you’re at the office, the Internet of Things grows. When cutting-edge garden tech allows you to water your herbs from halfway around the globe, the Internet of Things grows.

It is important to understand, though, that the IoT is not Skynet biding time to build its cyberspace army. The IoT is used to automate inventory and improve communications between people. It assists in search and rescue operations and monitor heart implants. Nonetheless, for all of the good that the IoT is capable of, it nurtures growing security risks as well.

So What is the Internet of Things?

The Internet of Things is an umbrella term describing the vast array of Internet-accessing devices that we interact with on a daily basis. This includes mobile devices, vehicles, buildings, thermostats, home appliances, street cameras, air purifiers, refrigerators, childrens’ toys, and much more. Objects that possess sensors, software, or microchips are known as cyber-physical systems and likely to fall under the IoT umbrella. The concept is hard to wrap your head around because it reaches across every industry and every channel one could imagine.

The great fear in the cyber security world in regards to the IoT is a potential for hackers to remotely access and control devices over networks shared by the IoT.

Welcome Aboard: An IoT Metaphor

Let’s picture the Internet of Things as a cruise liner. The klaxons sound in response to an engine room breach–in the case of the IoT, a hacker; in the case of our cruise liner, a hole in the haul—and seamen begin to combat the leak.

Water-tight hatches are sealed between various compartments of the ship, ensuring that water coming in through the engine room is unable to spread into neighboring compartments. However, in our IoT analogy, there’s an open pipe running from the engine room to the officers’ quarters because the sailors requested soda fountains. Another pipe runs from the engine room to the storage compartments because water is needed to humidify the air. A third set of pipes runs between the engine room and the ballast compartments for regulating buoyancy. Even though the maintenance team has sealed off all the main hatches between compartments, the leak continues to spread through the innumerable channels made possible by the demands of the crew.

Issues of IoT Vulnerability in the Real World


  • FBI Announcement for IoT Toys – On Monday the 17th, the Federal Bureau of Investigation issued a consumer notice to parents warning them of the threats associated with Internet-connected toys. As interactive toys grow in popularity, toys are being made with sensors, microchips, data storage, microphones, cameras, and more. The FBI warns that these types of toys may be used to compromise the privacy of children. The Public Service Announcement can be found here.
  • IoT Security is Expensive – The costs associated with IoT security are rapidly growing to keep pace with the sheer size of the Internet of Things and the ripe potential for bad guys to exploit it. According to a white paper published by Altman Vilandrie & Co., the IoT is projected to encompass 18,000,000,000 devices by 2022. That’s more than double the number of human beings on the planet. Altman Vilandrie also estimated that spending on IoT security will outgrow spending on “traditional” cyber security at a rate of nearly two and a half times.
  • Passenger Drones Over Dubai – And the award for “Most Terrifying Place to Learn About IoT Breaches” goes to… the inside of a passenger drone hovering hundreds of feet above the ground. Dubai has announced its intention to implement passenger-carrying quadcopters as exasperatingly luxurious taxis in the summer of 2018. Passengers will have no manual controls, relying instead on Internet-connected GPS to deliver them at their destination. Keep an eye out for this new cyber security threat to become a special effects whirlwind shoehorned into the next James Bond film!


Optimizing Security for the IoT

  • Disable UPnP – Many firewalls and routers possess a feature known as Universal Plug and Play (UPnP). This setting allows a device to plug into a network and configure itself, making it more convenient and mobile. However, this extra versatility comes at a price: security experts believe that UPnP may allow exploits to automatically jump from the IoT to the network during configuration. Once your appliance is positioned, it is a great idea to disable UPnP. Learn more about UPnP from our friends at Sophos.
  • Strengthen Your Passwords – Yes, this is the same advice we give to those seeking to optimize their more traditional cyber security. However, the IoT carries with it further complications in this arena: in many cases when one wants to set a password, they are presented with a numpad and asked to enter a 4-digit PIN. This can make it difficult to secure your devices with strong enough passwords. We suggest that you create a unique password for each device. Yes, it will mean that you have a lot more passwords to keep track of, but it does protect your data in case of a breach.
  • Patch Your Firmware – Wow, I think we’ve heard this one before too! Again we cannot stress enough the importance of keeping your security patches and firmware up to date. If you dissect most major cyber attacks, you will discover over and over and over that the affected demographics tends to gravitate around those who shrug and ignore the latest updates. In the IoT world, firmware may also sometimes be referred to as “microcode.”
  • Segregate IoT Devices to Your Guest Network – Many businesses now provide guest networks that remain overtly separate from their private network. Doing so provides the peace of mind that some schmuck on the street isn’t going to walk into your lobby, connect to your wireless network, and spread his nasty bugs around your system. If possible, try to quarantine as many IoT devices onto this guest network as possible. This way if a breach does occur, your most precious data is sheltered.

The cyber security industry absolutely buzzes with excitement, anxiety, and doubt when the discussion turns to the Internet of Things. It is an explosive matter. The IoT will continue to grow. Its ability to make our lives more convenient and connected will continue to grow. So too will the threats and vulnerabilities that it represents. Expect to see high-profile news stories revolving around Internet-connected objects and expect to see your budget in this area balloon as the IoT expands. From cars to toys to cameras, every industry and interest contributes to the ever-expanding galaxy that is the Internet of Things.

Firewalls.com is a value-added reseller of firewall appliances & a vendor of managed security and Firewall-as-a-Service support. Our engineers are rigorously trained and certified by all of the major manufacturers that we partner with. Whether you’re looking to add an appliance to your security set-up or seek ongoing support from seasoned experts, we can provide the security solutions necessary to get you secure and keep you secure. Contact one of our knowledgeable sales staff to answer any questions you may have about your network, our firewalls, or the Internet of Things!

You can also follow us on Twitter and Facebook.


How One Company is Standing Out in the Crowd: Capture ATP makes other sandboxes look small

Sandbox technology, which you can find a definition for on our Network Security Glossary, is the latest buzzword clawing its way through the info sec community. The rise of cloud-based threat protection is here and already the major players are proving they intend to maintain their seat in the pantheon of info sec titans. Perhaps the most successful showing, however, is from SonicWall. Capture ATP is making a real impact thanks to consistent successes in the face of a spike in high-profile ransomware attacks. ATP stands for Advanced Threat Protection and with Capture ATP that is exactly what you get.

Some major feats so far for the emerging cyber security champion include protecting its users from Petya thanks to having detected threat signatures a year in advance and silencing the encroachment of Eternal Blue exploits in April 2017, just before WannaCry. The bottom line is that Capture ATP is the real deal.

So how does it work?

Capture ATP detects suspicious code right at the gateways of your network and quarantines them in a virtual emulation of your system, allowing threats to unpack themselves and betray their nasty secrets in a safe sandbox environment where they can be monitored, tested, and neutralized.

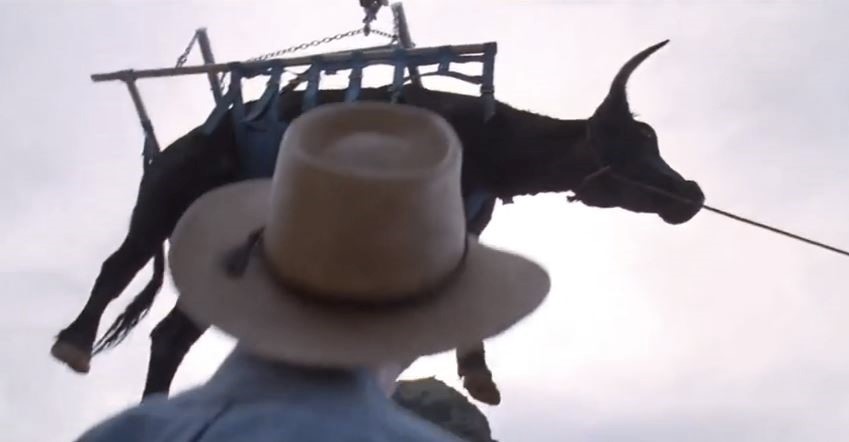
Remember this scene from Jurassic Park?

feeding cows to ransomware

It’s sort of like that: corral potential threats into a cage, then let them openly demonstrate their viciousness against disposable targets while we watch at a distance.

Okay, sandboxes aren’t new. So what makes Capture ATP stand out among the crowd?

Most sandbox systems run suspicious threats through one engine before giving threats the thumbs up or thumbs down. In these cases, you are relying on the manufacturers’ inspection systems to get it right the first time, every time. SonicWall seems to understand that getting another pair of eyes on an issue can be beneficial. In addition to SonicWall’s own threat-detecting engine, Capture ATP scans are backed up by LastLine Breach Detection and VMRay Analyzer engines that provide a second and third opinion before giving a verdict on potential threats.

I have standard anti-virus protection already. Why do I need ATP?

AV clients are great for blocking known threats. But cyber criminals of 2017 are shape-shifters and masters of disguise. The bad guys are becoming much better at sneaking through your gateways and in response, security protocol must tighten. Where once stateful inspection was sufficient, serious security firms are now demanding nothing less than deep packet inspection. As the enemy evolves, so too must the good guys.

The greatest threat to your network is now from zero-day threats. Zero-day threats are cyber attacks that target exploits that have, at the time of the attack, not been discovered or discussed widely by the cyber security community. These are attacks that could not properly be prepared for because the danger was not yet apparent or understood. With Capture ATP, suspicious code is stopped at the gateway and held in custody until an official verdict is determined. This is better-safe-than-sorry security that errs on the side of caution. With Petya, Wannacry, Eternal Blue, and other major exploits in the global spotlight, this understandably draconian style of network security is saving the day again and again for those of us under its protection.

SonicWall’s motto for the sandbox campaign is “Fear Less” and with Capture ATP, it seems more a promise than a tagline. Let’s face it, businesses everywhere just want to get this ransomware thing behind them so they can get back to taking care of customers and making money. Capture ATP cannot cure the ills of the cyber world, but it can take the pressure off of small to medium-sized businesses and enterprises alike so that we can stop worrying over every email attachment and get back to worrying about growth, customer relationships, and values.

capture atp sonicwall firewall


GET THE CAPTURE ATP DATASHEET


Ransomware Warfare: How to protect your files from hostage takers

Ransomware represents one of the greatest threats to your data with studies indicating that ransom takers are specifically turning their focus towards smaller networks. Fox Business claims that 43% of ransomware targets in 2015 were small to medium-sized businesses. With the recent trouncing received by the IT world at the hands of WannaCry, network invaders are becoming emboldened to encrypt your data and stash it away until you pay up. And with a staggering 70% of business owners deciding to fork over the money, the incentive is strong. Ransomware is making a killing and your network may be next in front of the firing squad. But with the right know-how and cyber security culture in your office, you can survive the bloody war against malware.

Firewalls Ransomware 101
“If you know the enemy and know yourself, you need not fear the result of a hundred battles.” –Sun Tzu, about ransomware


How to Stay Safe

File Backup & Recovery Process

Businesses often become so wrapped up in the fight against malware that they forget the old-fashioned dangers of the world: floods, fires, famines (okay, maybe not so much), break-ins, mobile devices dropped down airplane toilets, tablets crushed in a fit of furious rage following a nasty Yelp review. The list goes on. Luckily, your IT department has years worth of readily available file backups, right? Just as we continue practicing tornado drills and fire evacuations, we should perpetually practice procedures for catastrophic data loss. Understand your recovery process and ensure that file backup is delegated to an accountable party. If the worst should happen and you find your files locked away by the Ransomware Bogeyman, you can let out a sigh of relief knowing that multiple copies of your precious data are stowed away in the closet or on the cloud.

Encryption

Did you know that banks leave thousands of dollars in cash just sitting on the street corner every day? Yes, ATMS nationwide go unrobbed routinely because they are locked down tighter than Fort Knox. Good news! This approach can work for your data as well. By encrypting the data on your network, you can prevent network intruders from walking away with your files even if they manage to force their way into the system. Imagine the look on a burglar’s face when he walks into a house where everything is locked up in heavy-duty safes.

Disable Macros

Microsoft disabled the automatic execution of macros in email attachments years ago, and for good reason. An example of social engineering, some phishers will attempt to persuade users into enabling macros on email attachments. If ever you are encouraged to enable macros, the request should be treated as more than a red flag. It’s a whole red flag factory. Double-check that your email settings have disabled macros.

Attachments

The classic rule of thumb for attachments is to never open one if you’re unfamiliar with the sender. VBA droppers are an increasingly common delivery system for ransomware and can be packed away within several layers of file types like Russian nesting dolls or a data-thieving turducken. Even if you receive a harmless PDF file, that PDF file can hold an executable to launch a Microsoft Word file, which in turn is setup to launch an RTF file, and so forth until a VBA Dropper lands on your computer before you know what’s happened. So yes, it is time to have another all-hands meeting to drone on and on about not opening attachments from strangers. Seriously, your users are still opening suspicious attachments. Right this second (probably).

Administrator Access

Your custodian doesn’t require administrator-level access to your network. In fact, very few of your employees should be given this level of clearance. The reason why? If attackers do manage to break in, you don’t want all of your users walking around with skeleton keys. Mitigate potential damage to your system by ensuring that employees are able to access and utilize the tools they need without requiring administrative access. For a better look at how not to tighten up your administrative model, check out how the NSA took a crack at it.

System Updates & Patches

WannaCry was a painful learning experience for many network administrators. For those of you still unaware, Microsoft released a patch that prevented the exploits targeted by WannaCry on March 14, 2017, a full two months before the May 12th ransomworm tore the world a new one. There is a very solid line separating those affected by the worm and those that were not: those of us who made it out unscathed (all of Firewalls.com’s customers, btw) kept our security patches up to date!

The war against ransomware is never-ending and we understand if morale is low. But your network is too important to leave to chance. The data doesn’t lie: ransomware attacks are on the rise and their campaign is turning towards small and medium-sized businesses. Let Firewalls.com be your private army in the battle against ransomware. We’re mean. We’re lean. We’re bad guy fighting machines.

LEARN HOW FIREWALLS.COM CAN PROTECT YOUR NETWORK


6 things you could be doing instead of configuring a firewall

Packet filtering, stateful inspections, proxy service–the world of network security is bristling with intimidating terminology and stat/spec jargon. Wading into the deep end of online security protocol means more than just an afternoon’s worth of study. And that’s just for picking which appliance to buy. When it comes to setting up your new firewall appliance, why not claw back some of your schedule with our configuration service?

While the stalwart do-it-yourself master watching the Firewalls.com how-to videos may be looking to throw away their weekend configuring a new firewall, a busy business professional has enough on their plate already and should be looking to delegate firewall configuration to someone who already knows their way around a security setup. And who better to delegate to than Firewalls.com’s certified engineers who specialize in providing your company with expert configuration services.

Don’t spend several hours configuring your new firewall. Hand off the legwork to an expert. And instead of banging your head against the racks, maybe you can use your unexpected free time on one of these 6 activities:

Firewalls Client Phone

Spend some 1-on-1 time with your clients

We all love to hear from our customers, but some days your schedule is just too chaotic to thumb through the Rolodex. But now that you’ve pawned off a few hours worth of configuration work onto a professional services team, you have plenty of time to pick up your handset and reach out to those precious accounts. And since you’re already on the phone, you can give our engineers a ring if you run into any issues with your security appliance. Configuration services are accompanied by unlimited, on-going phone support.

Firewalls War Battle

Have an office-wide Nerf war

Account manager getting on your case about lead flow? Maybe they’ll think twice about complaining after you unload a clip of foam fury on them. While our Firewalls.com certified engineers are securing your network, your team can be setting a perimeter around the office armed with the latest dart-throwers and N-Strike blasters.

Firewalls Google Alerts Notification

Set up Google Alerts for your brand

If your ears are burning, it means someone is talking about you. And if someone is talking about your company, you want to know about it. Google Alerts provides a service to set up automatic email alerts whenever your chosen keywords are published on the web. Stay on the bleeding edge of industry news by filling your inbox with up-to-the-minute articles. You stay a step ahead of the competition, we’ll watch your back.

Firewalls Hoverboard Skate

Hoverboard around the office park

Studies are increasingly claiming that sitting is the new smoking, so why not get up and stretch your legs? Better yet, put those legs atop a hoverboard and roll around the office park, provoking the ire and jealousy of those poor office drones watching from the windows. They too could be outside if they weren’t so busy configuring firewalls. If only they had thought ahead like you.

Firewalls Thought Leaders

Catch up on industry thought leaders

Thought leaders. The buzzword is all the rage in the world of LinkedIn. Whether you’re looking to catch up on a few months’ worth of blogs, industry articles, or the latest Tweets, you now have a treasure chest of time to uncover the leaders in your industry. Steal their knowledge, ride the coattails of their experience, and stay hip on emerging lingo. You have time enough to both lead and read, thanks to a configuration service.

Firewalls Reddit

Waste time on Reddit

What’s the harm in letting your brain cool down from time to time? Admit it, we all indulge in a bit of Internet tomfoolery. Whether you’re catching up on the news, getting heated over politics, or just cruising for memes, you certainly won’t feel bad about wasting time thanks to the hours you saved with professional services.

ProTip: You can’t waste time you didn’t plan on having in the first place!

Whether you devote your newfound free time to business or pleasure, you certainly shouldn’t be wasting a day configuring your firewall. Take advantage of Firewalls.com’s Configuration Service for your SonicWall, Sophos, or WatchGuard appliances. Firewalls.com customers can opt for either Standard or Advanced Configuration service, based on the specific needs of your company. We offer a wide variety of service options beyond simple configurations.

Features at a Glance:

  • Proprietary 50-Step Configuration checklist
  • Setup and testing of VPN tunnels
  • Configuration of wireless access points
  • Granular content filtering & bandwidth prioritization

LEARN MORE ABOUT EFFORTLESS DEPLOYMENT


5 Tips to Speed Up SonicWall’s CFS Content Filtering

Optimizing CFS

Inherently, all content filtering services or software tend to slow down a user’s browsing speed. SonicWall’s CFS filtering service is no exception. The overall decrease in speed is caused by DNS queries and URL database lookups that need to be performed to allow it to categorize the website being visited.

So how can you speed up the process? In this video we share 5 top tips designed to optimize and increase the performance of your SonicWall when you’re using the content filtering service.

Blog Banner General Buy Now Red-High-Quality


Shop the latest SonicWall Content Filtering options.

Learn more about what content filtering can do for your network.


← Older posts Newer posts →